Zero Trust: Building defense for the perimeter-less era
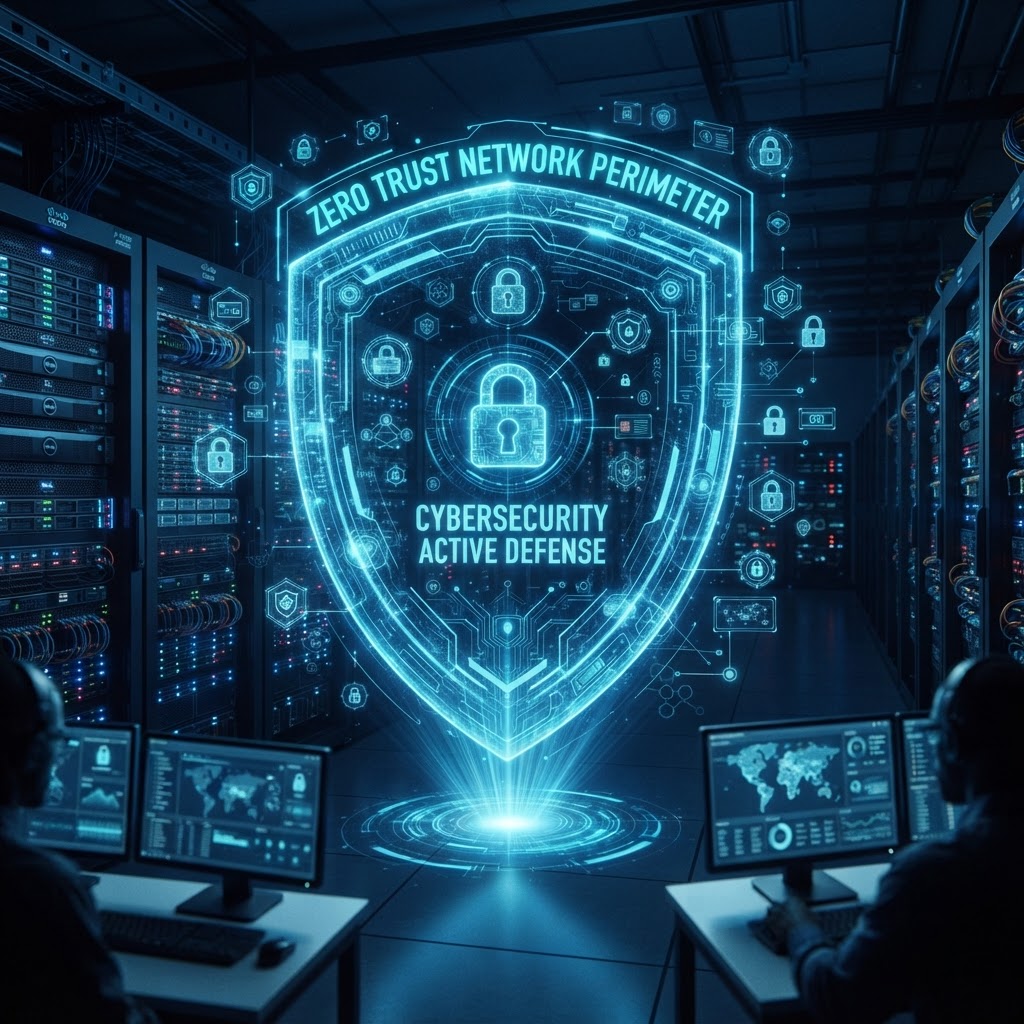
Why every enterprise must rethink trust boundaries in a cloud-first, remote-working world.
The traditional network perimeter dissolved the moment workloads left the data center. With users on home networks, applications in multiple clouds and APIs connecting partners, the old model of a trusted interior and hostile exterior no longer holds.
Zero Trust replaces implicit trust with continuous verification. Every request, regardless of source, is authenticated, authorized and inspected before it reaches a resource. Identity becomes the new perimeter, and least-privilege access is enforced dynamically based on context, device posture and risk.
For Quantum Institute clients we implement Zero Trust around five pillars: identity, devices, networks, applications and data. Micro-segmentation limits lateral movement, while conditional access policies adapt in real time. The result is an architecture where a compromised laptop or leaked credential no longer equals a breach, because no single failure grants broad access.
The journey is incremental: map the attack surface, classify data, enforce strong identity, segment networks, then continuously monitor. Done right, Zero Trust reduces blast radius and makes security a business enabler rather than a gatekeeper.